M&A Due Diligence Beyond Financials: Building a Governance Risk Profile Before You Buy
Financial due diligence tells you what a company earned. Governance due diligence tells you whether it will keep earning it. Most acquirers invest heavily in the former and gloss over the latter, then spend years discovering the compliance gaps, control failures, and regulatory risks that a proper governance assessment would have identified before completion.
Every acquisition involves financial due diligence. The buyer's accountants spend weeks analysing revenue quality, working capital, debt, contingent liabilities, and normalised earnings. The output is a detailed financial model that values the target and identifies the financial risks of the transaction.
Almost no acquisition involves equivalent governance due diligence. The buyer's lawyers review material contracts, pending litigation, and regulatory licences. The compliance team does a high-level scan of policies and procedures. Someone reviews the organisational chart. And that is typically where governance due diligence ends.
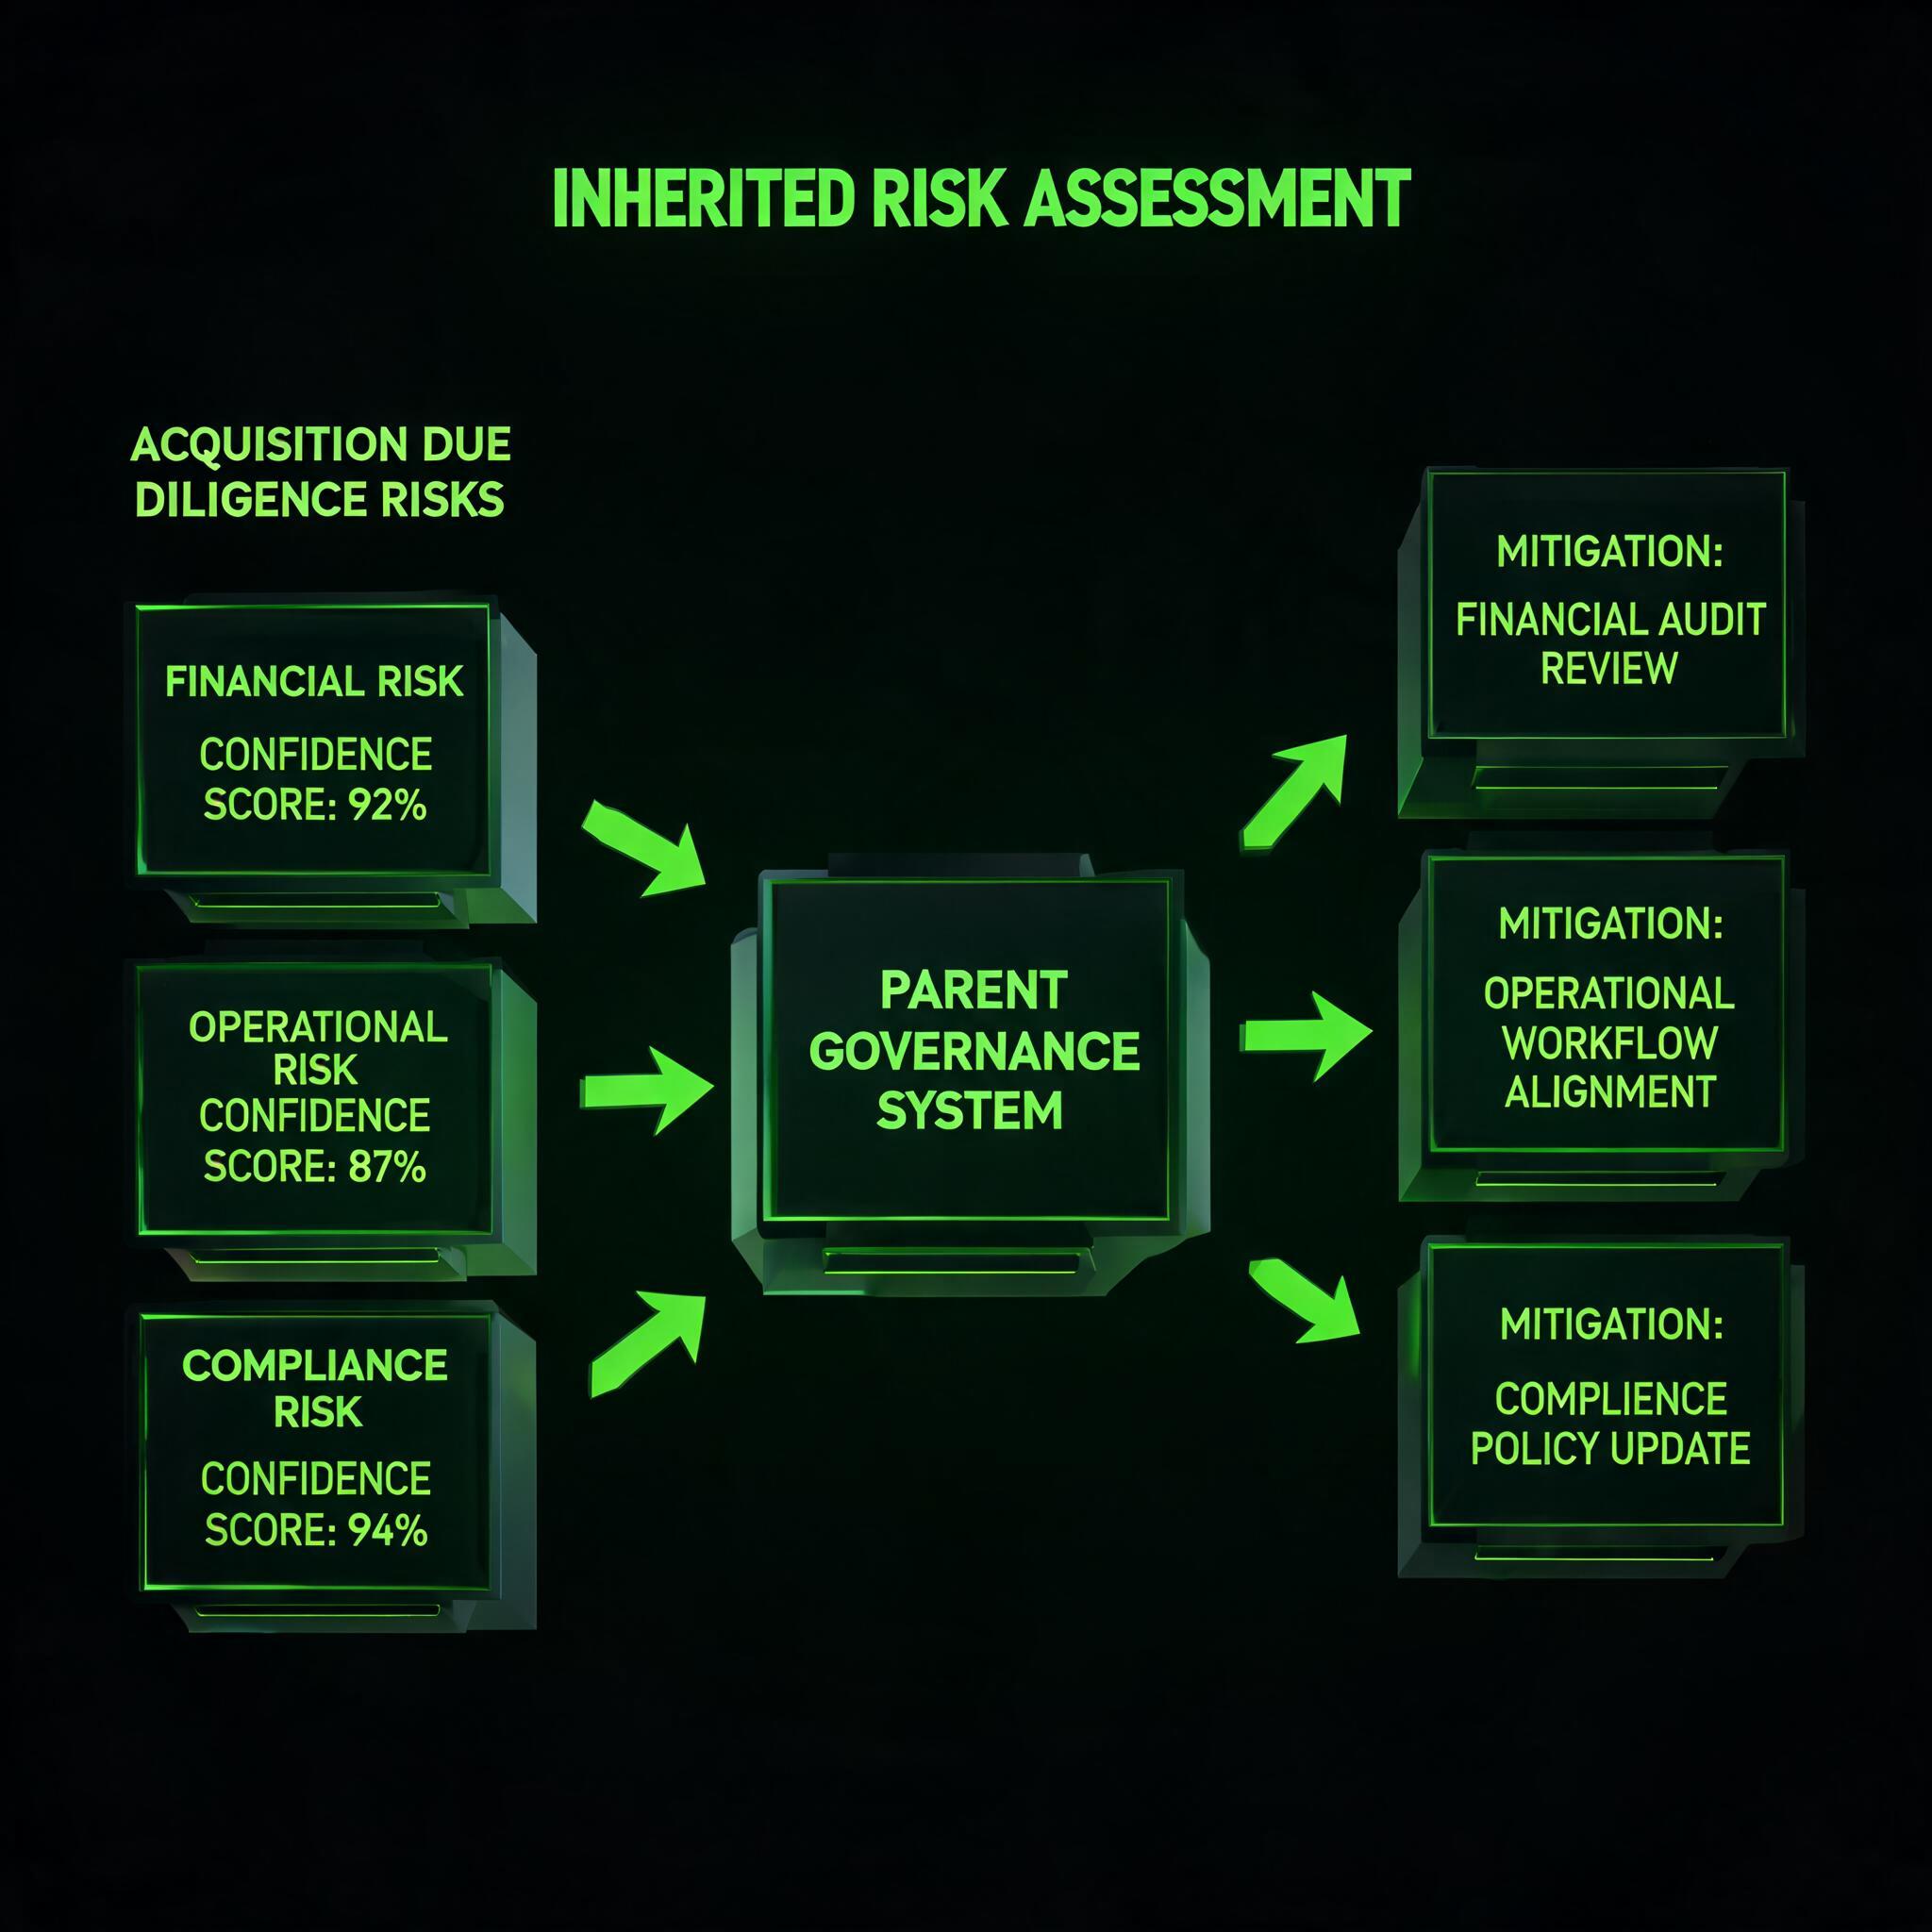
This asymmetry is expensive. Post-acquisition, the governance gaps that nobody assessed before completion become integration problems that cost time, money, and executive attention. Undocumented processes. Missing controls. Non-compliant data handling. Expired regulatory certifications. Unresolved audit findings. These are not surprises. They are predictable consequences of a due diligence process that looked at the numbers and ignored the governance architecture.
What Financial Due Diligence Misses
Financial due diligence is designed to answer a specific question: what is the target worth? It analyses historical financial performance, adjusts for non-recurring items, models future cash flows, and identifies financial risks (debt covenants, tax exposures, pension liabilities). It is thorough within its scope.
But its scope does not include the governance architecture that sustains the financial performance. Consider what falls outside a standard financial due diligence engagement:
Control framework maturity. Does the target have a documented internal control framework? Are controls tested regularly? Are control failures remediated within defined timescales? A target can have excellent financial results and a weak control environment: the results are accurate today, but the control gaps create risk that will materialise tomorrow.
Regulatory compliance depth. Legal due diligence confirms that the target holds the necessary licences and authorisations. It does not assess whether the target's ongoing compliance activities are adequate to maintain those licences. A firm that passed its last regulatory inspection two years ago may have accumulated compliance gaps since then that the buyer will inherit.
Data governance maturity. In 2026, data is often the most valuable asset in an acquisition. But data governance maturity (data quality, data lineage, data protection compliance, consent management, cross-border data transfer mechanisms) is rarely assessed with the same rigour as the financial value of the data asset. The buyer pays for a data asset that may be non-compliant, poorly governed, or legally constrained in ways that reduce its practical value.
Third-party risk exposure. The target's financial performance may depend on relationships with suppliers, outsourced service providers, or technology vendors. Financial due diligence assesses material contracts. It does not assess the governance of those relationships: whether the target has adequate vendor risk management, service level monitoring, and exit plans.
Key person dependencies. Financial due diligence identifies key employees for retention purposes. Governance due diligence would identify key person dependencies in the control framework: processes that depend on individual knowledge rather than documented procedures. These dependencies create operational risk that becomes critical during post-acquisition integration when key people often leave.
The Cost of Governance Gaps Post-Acquisition
Governance gaps discovered after completion create three categories of cost:
Direct remediation cost. Building the controls, policies, procedures, and governance structures that the target should have had. This includes documenting undocumented processes, implementing missing controls, building compliance functions, and deploying governance technology. These costs are rarely budgeted in the integration plan because they were not identified in due diligence.
Regulatory cost. If the target's compliance gaps result in regulatory action, the buyer inherits the consequences. Fines, enforcement actions, mandatory remediation programmes, and increased supervisory attention all affect the buyer, not the seller. In regulated sectors, the buyer may also face regulatory challenge to the acquisition itself if the governance gaps are severe enough to raise questions about the combined entity's fitness.
Integration delay cost. Governance gaps slow integration. If the target's processes are undocumented, the integration team cannot map them to the buyer's processes. If controls are missing or ineffective, the integration team must build them before the combined operation can function safely. If data governance is weak, the data migration that was supposed to take three months takes twelve. Every month of integration delay reduces the value of the acquisition.
Building a Governance Risk Profile
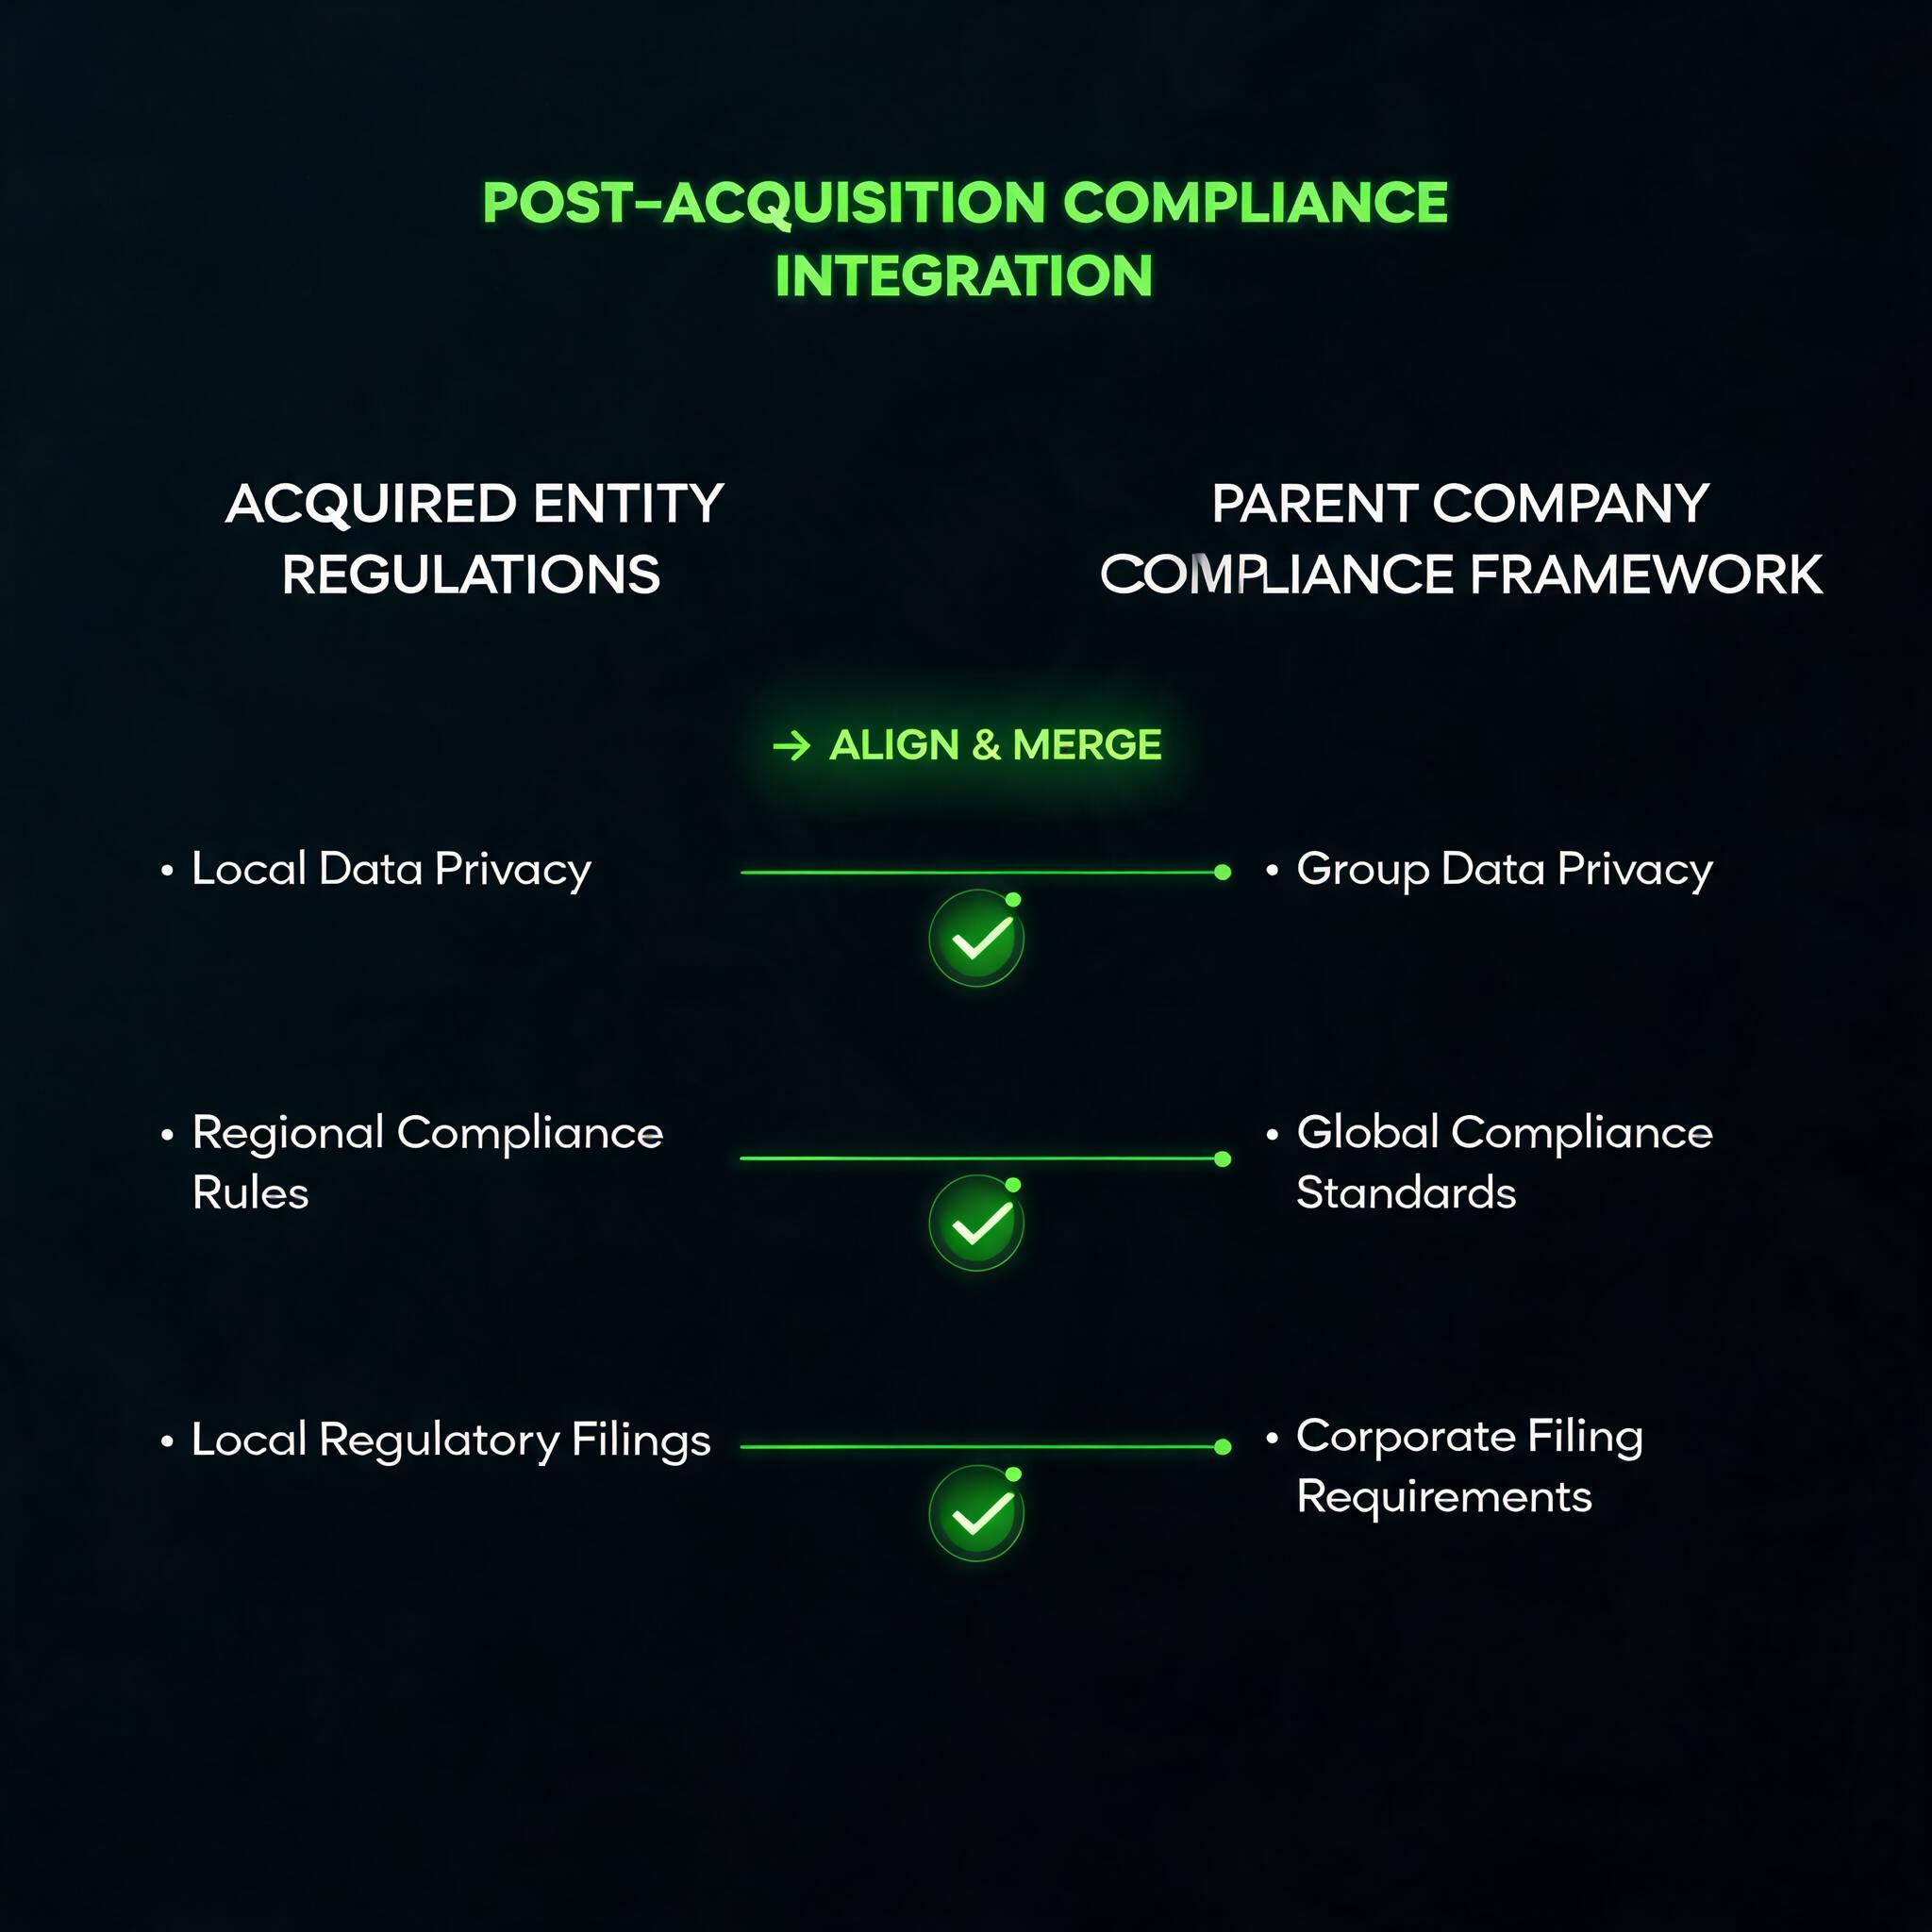
A governance risk profile is a structured assessment of the target's governance maturity across the dimensions that matter for post-acquisition integration. It is not a replacement for financial due diligence or legal due diligence. It is a complement that addresses the governance dimensions those processes miss.
The governance risk profile assesses six dimensions:
1. Control Framework Maturity
Is there a documented control framework? How many controls are defined? What percentage have been tested in the last 12 months? What is the failure rate? What is the average remediation time for control failures? This dimension tells the buyer how much work is needed to bring the target's controls to the buyer's standard.
2. Regulatory Compliance Posture
What regulatory obligations does the target operate under? For each obligation, what is the compliance status (fully compliant, partially compliant, non-compliant, untested)? Are there open regulatory actions, remediation programmes, or supervisory concerns? What is the cost of maintaining compliance post-acquisition?
3. Data Governance Maturity
What personal data does the target hold? Under what legal basis? Is consent management documented and defensible? Are cross-border data transfers compliant with current data protection law? What is the quality of the data assets (completeness, accuracy, timeliness, consistency)? What data governance tooling and processes are in place?
4. Third-Party Risk Exposure
Who are the target's critical suppliers and service providers? Are there documented contracts with appropriate service levels, liability provisions, and exit rights? Is there a vendor risk assessment process? Have critical vendors been assessed recently? Are there concentration risks (single-source dependencies)?
5. Process Documentation and Key Person Dependency
Are critical business processes documented? For each process, is the documentation current? Are there key person dependencies where individual knowledge is the only record of how a process works? This dimension predicts the integration risk: undocumented processes with key person dependencies are the highest-risk items in any integration.
6. Governance Culture Indicators
Does the target have a functioning governance committee structure? Are governance meetings held regularly with documented minutes and action tracking? Is there a compliance reporting culture (incident reporting, whistleblowing, near-miss reporting)? Is there a governance budget? Governance culture indicators predict whether the governance improvements required post-acquisition will be adopted by the target's workforce or resisted.
How Simplif-i Supports M&A Governance Due Diligence
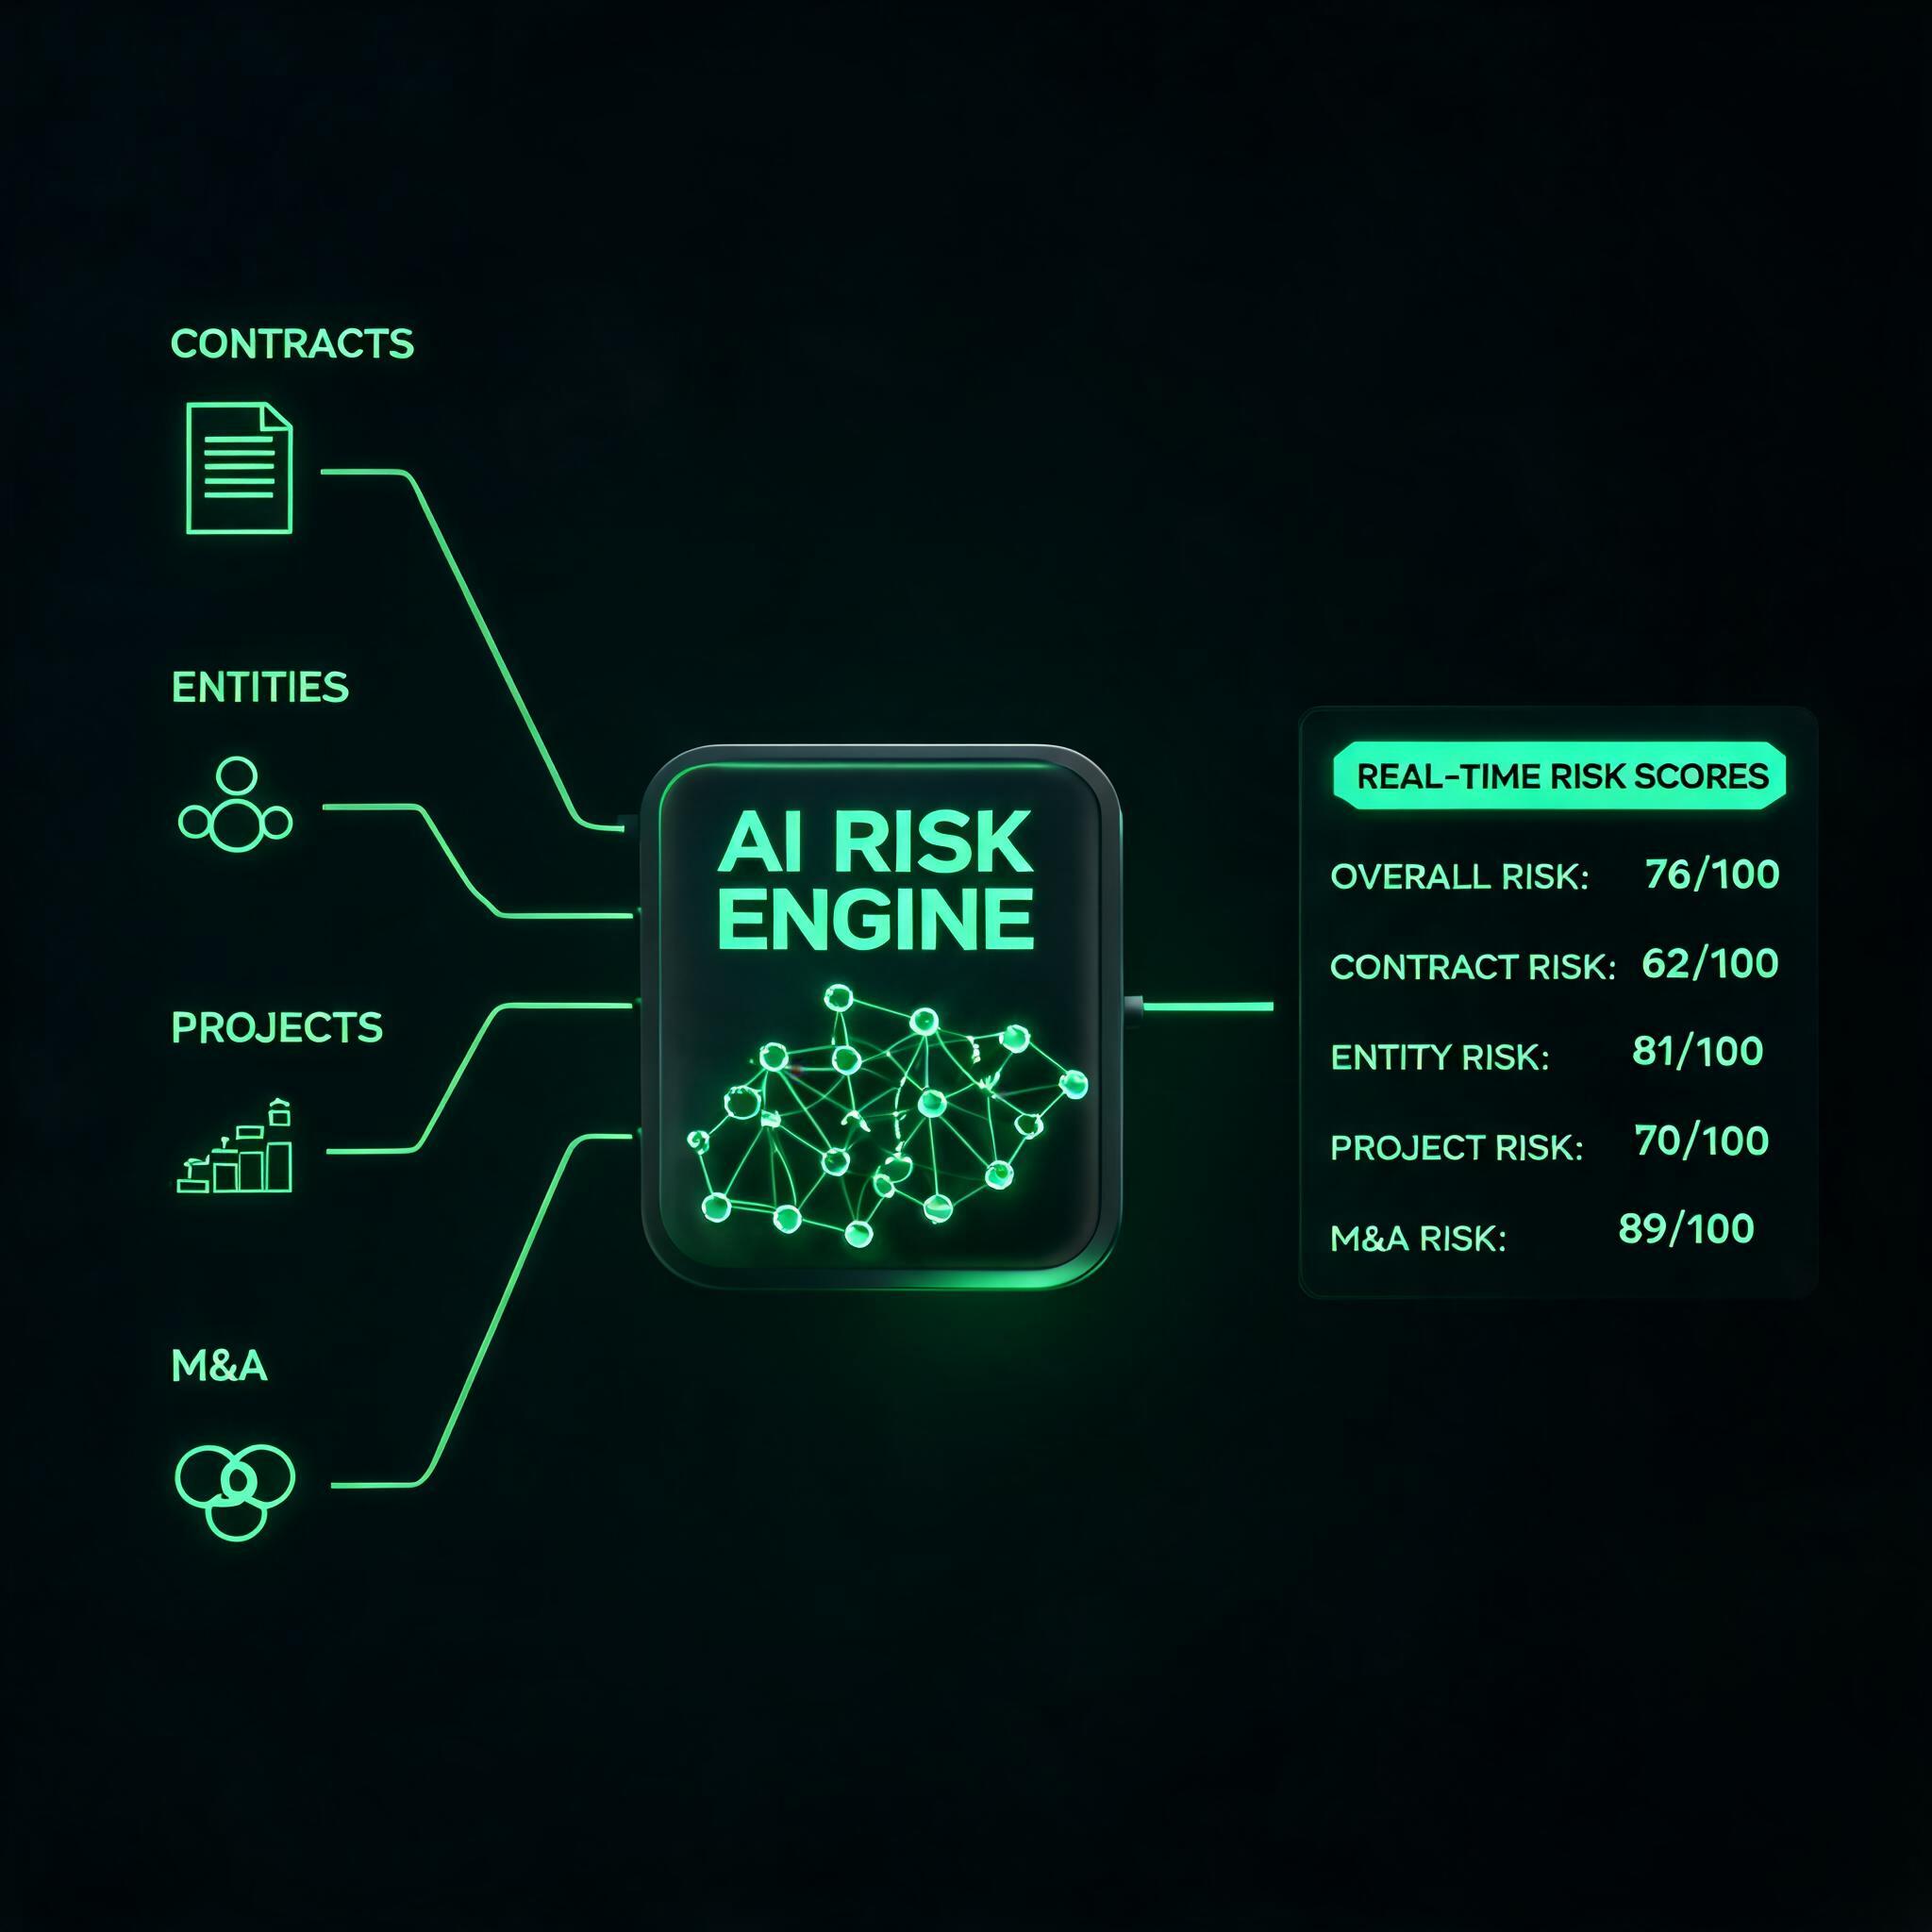
Simplif-i's M&A module provides the structure and tooling to build a governance risk profile during due diligence and carry it through into integration planning:
-
Due diligence workspace: A secure, compartmentalised workspace where the due diligence team can document findings across all six governance dimensions, assign maturity scores, and identify material governance risks for the investment committee.
-
Governance gap register: A structured register of governance gaps identified during due diligence, each linked to a remediation cost estimate, an integration dependency, and an owner. This register becomes the governance integration plan post-completion.
-
Risk-adjusted valuation inputs: Governance gaps are quantified as contingent costs and fed into the financial model as risk adjustments. A control framework that needs building has a cost. A compliance gap that may result in regulatory action has an expected value. These inputs make the acquisition price reflect governance reality, not just financial history.
-
Integration playbook generation: Based on the governance risk profile, Simplif-i generates an integration playbook that sequences governance remediation activities, assigns owners, sets milestones, and tracks progress. The playbook is integrated with the PMO module so governance integration is managed alongside operational, technology, and people integration.
The Pre-Acquisition Governance Audit
For acquirers who want maximum governance visibility before completion, Simplif-i supports a pre-acquisition governance audit. This is a structured assessment, conducted in the data room, that evaluates the target against the buyer's governance standards across all six dimensions.
The output is a governance risk profile report that includes:
-
An overall governance maturity score for the target
-
A dimension-by-dimension breakdown with specific findings
-
A governance gap register with estimated remediation costs
-
A governance risk register with enterprise risk implications
-
An integration complexity assessment based on the governance delta between buyer and target
-
Recommended conditions, warranties, or indemnities to address material governance gaps in the sale agreement
This report gives the investment committee a complete picture: not just what the target is worth financially, but what it will cost to bring to the buyer's governance standard and what risks the buyer inherits if it does not.
The Bottom Line
Financial due diligence tells you what you are buying. Governance due diligence tells you what you are inheriting. The companies that consistently create value from acquisitions are the ones that assess both with equal rigour.
If your due diligence process produces a 200-page financial model and a two-page governance summary, your acquisition price reflects financial reality and governance fiction. The governance gaps are still there. You just agreed to pay for them without knowing what they will cost.
Build the governance risk profile before you sign. Not after.
Compliance, simplif-i'd.
Connect due diligence and integration
Bring due diligence and integration planning together in Simplif-i.