Compliance is Your Secret Weapon: Turning GRC Into a Sales Enabler
Governance, Risk, and Compliance is usually seen as a cost centre. In the mid-market, it is actually a profit centre. Organisations that can prove their compliance win bigger deals faster by removing friction from the sales cycle.
Most people see GRC as a shield to hide behind. I see it as a sword to win with. If you can show a prospect your ISO 27001 or SOC 2 certification with a single click, you have just shortened your sales cycle by weeks.
Definition: GRC (Governance, Risk, and Compliance) is a strategy for managing an organisation's overall governance, enterprise risk management, and compliance with regulations.
Action List for COOs:
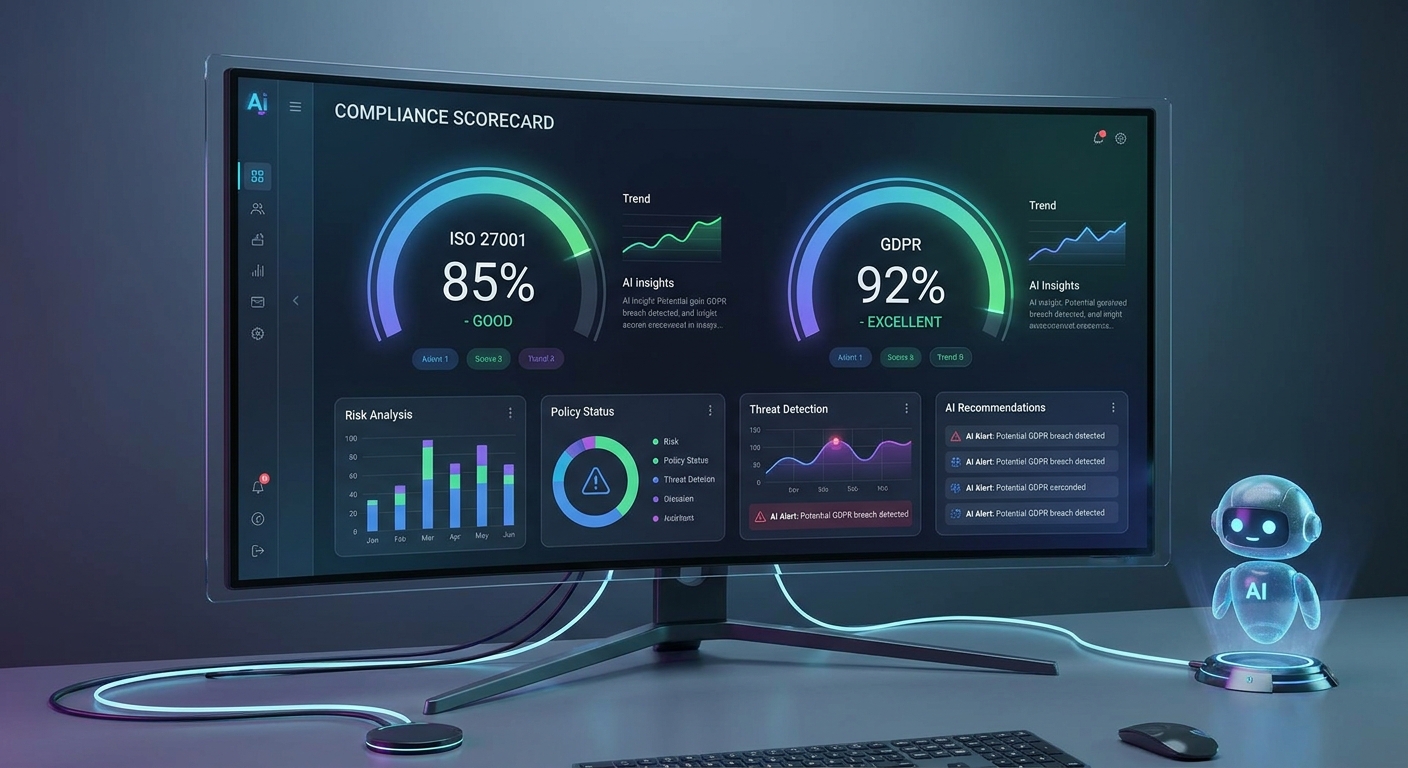
- Automate evidence collection: Stop paying high-value employees to take screenshots. Use AI to collect and validate evidence.
- Cross-map your controls: Do not manage ISO 27001 and GDPR in silos. Map your controls once and apply them across all frameworks.
- Real-time risk visibility: A risk register from last quarter is useless. You need a live signal of your operational health.
- Policy automation: Ensure every employee has read and acknowledged your policies through automated workflows.
Founding Member Offer: Turn your compliance into a competitive advantage for £149 as a Founding Member.
✨ Recommended For You
Audit Readiness as a Service: Turning GRC from Cost to Capital
Compliance should not be a once-a-year scramble. Learn how continuous GRC monitoring turns audit readiness into a competitive advantage.
Continuous Compliance: Turning GRC from a Shield into a Sword
Stop the annual audit panic. Discover how continuous compliance and automated GRC turn regulatory requirements into a competitive advantage.
How to align governance, risk, and compliance effectively
Discover what governance risk compliance is and learn how to align these critical disciplines for better efficiency and accountability.
Bring your compliance work together
Organise requirements, supporting evidence and follow-up work in Simplif-i.